Yes — but only if the AI tools being used are specifically configured for HIPAA compliance, which the free, consumer versions of tools like ChatGPT and Gemini are not. This distinction is the single most important thing for a practice owner or office manager to understand before adopting AI in any capacity. The question isn’t whether AI can be used safely in a medical or dental practice — it’s whether the specific tool and deployment in front of you was actually built with that responsibility in mind.
This article walks through where practices are already using AI (often without realizing the compliance implications), what HIPAA-aligned AI actually requires, and where the real opportunity is for practices that get this right.
Where AI Is Already Being Used in Practices Today
Even in practices that haven’t formally adopted AI, it’s often already in use informally. A front desk employee might paste a patient’s intake notes into a free chatbot to help draft a summary. A provider might use a consumer AI tool to help phrase a difficult conversation with a patient. An office manager might upload a spreadsheet of patient appointment data to help analyze no-show patterns.
Every one of these examples is well-intentioned, and every one of them creates potential HIPAA exposure the moment protected health information (PHI) enters a tool that wasn’t built to handle it. This is exactly what’s often referred to as shadow AI — AI use that’s happening without oversight, policy, or the technical controls needed to keep it compliant.
Why Free, Consumer AI Tools Are Not HIPAA-Compliant by Default
HIPAA compliance isn’t a general feature — it requires a formal Business Associate Agreement (BAA) between a covered entity (like a medical or dental practice) and any vendor that handles PHI on its behalf. Free, consumer-tier versions of popular AI tools generally do not offer a BAA, and without one, using them to process PHI is a compliance violation regardless of how careful or well-intentioned the employee was.
This matters because the risk isn’t really about the AI technology itself — it’s about the terms and infrastructure behind a specific tool. The same underlying AI capability can be perfectly safe in one configuration and a compliance violation in another, depending on whether it’s backed by a BAA, proper data handling agreements, and audit logging.
The Real Opportunity: Where AI Genuinely Helps a Practice
Once the compliance piece is handled correctly, AI automation offers real, practical benefits for medical and dental practices, particularly around the operational pain points that eat staff time every day:
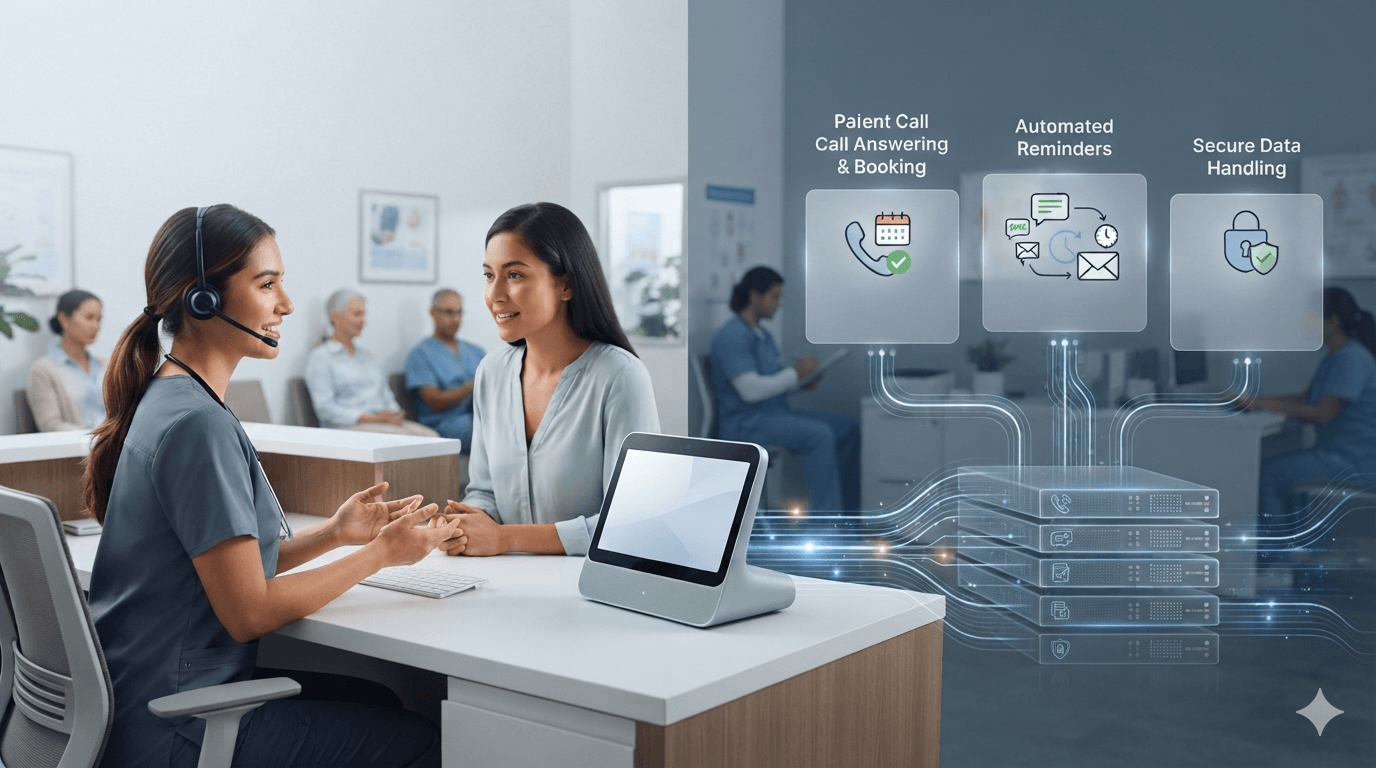
Patient call answering and appointment booking. Practices routinely see call volume spike at the same times patients are most likely to try to reach them — early morning, lunch, and right after work. An AI phone assistant can answer every call and book appointments directly into the practice’s scheduling system, 24 hours a day, without adding front-desk staff.
Automated reminders and recall campaigns. No-shows are one of the most persistent revenue drains in healthcare and dental practices. Automated reminder sequences — and recall outreach for patients who are overdue for a cleaning, checkup, or follow-up — reduce no-show rates without requiring staff to manually track and call every patient.
Freeing the front desk to focus on patients physically in the office. When phone volume is absorbed by an AI assistant, front-desk staff can give full attention to the patients standing in front of them instead of splitting focus between the counter and a ringing phone.
A HIPAA-aligned internal AI environment for staff. Rather than leaving employees to find their own AI tools for drafting patient communications or summarizing notes, a properly governed practice can provide a sanctioned AI environment that staff are encouraged to use — one that’s actually covered by the necessary compliance agreements.
What “HIPAA-Aligned AI” Actually Requires
For a practice owner evaluating any AI vendor or tool, a few specific things should be treated as non-negotiable:
- A signed Business Associate Agreement (BAA) with any vendor whose AI tool will touch PHI in any form.
- Data handling that keeps PHI inside a controlled environment — not routed through consumer-grade tools or stored on infrastructure the practice has no visibility into.
- Access controls and audit logging, so there’s a clear, defensible record of who accessed what patient information, when, and through which tool.
- A clear policy — backed by technical enforcement, not just a written document — governing which AI tools staff are permitted to use and for what purposes.
That last point matters more than most practices initially realize. A written AI policy that isn’t backed by any actual technical restriction relies entirely on staff remembering and following it under time pressure — which is exactly the scenario where shadow AI use tends to happen.
A Practical Way to Think About Risk vs. Reward
It’s tempting for practice owners to respond to the compliance risk by banning AI tools outright. In practice, this rarely eliminates the actual behavior — staff under time pressure will often keep using whatever tool gets the job done fastest, just without telling anyone. That’s a worse outcome than having no policy at all, because it removes visibility along with the illusion of control.
A more effective approach pairs two things: a sanctioned, HIPAA-aligned AI environment that’s genuinely useful for staff, and real technical restrictions — not just a memo — on accessing unsanctioned public AI tools with PHI. This is the foundation of proper AI automation for business in a healthcare context: giving a practice the productivity benefits of AI while keeping patient data inside a compliant, controlled environment.
Questions Every Practice Owner Should Be Asking Right Now
- Do we have a written AI usage policy, and — more importantly — is there any technical control actually enforcing it?
- Have we asked staff directly what AI tools they’re currently using, informally or otherwise, for anything related to patient information?
- Do any of our current AI tools have a signed BAA in place? If the answer is no for a tool touching PHI, that’s an active compliance gap today, not a future risk.
- Would a HIPAA audit find a clear, logged record of how AI is being used across the practice — or would it find nothing at all?
Practices that can’t confidently answer these questions have a real, current gap worth addressing before it becomes a breach report.
Getting Started the Right Way
The practices that adopt AI most successfully tend to address governance and productivity together, rather than bolting security on after the fact. A useful starting point is a straightforward AI automation for business assessment focused specifically on where a practice is losing time — missed calls, no-shows, front-desk overload — paired with a review of exactly how AI is currently being used, sanctioned or not.
Frequently Asked Questions
Is it illegal to use ChatGPT in a medical or dental practice? Using ChatGPT itself isn’t illegal, but entering protected health information into a free, consumer-tier version without a Business Associate Agreement in place is a HIPAA violation, since there’s no compliance coverage for that data.
What is a Business Associate Agreement, and why does it matter for AI tools? A BAA is a legally required contract between a healthcare provider and any vendor that handles PHI on its behalf. It sets out how that data must be protected and used — without one, using a tool to process PHI is a compliance violation regardless of intent.
Can AI phone assistants actually book appointments correctly for a medical practice? Yes, when properly integrated with the practice’s scheduling system, an AI assistant can check availability and book appointments directly, the same way a front-desk employee would.
Does using AI automation reduce staff jobs at a practice? In most successful deployments, AI absorbs call overflow and repetitive scheduling tasks, freeing front-desk staff to focus on in-person patients and higher-value tasks rather than eliminating roles.
How do we find out if AI is already being used informally in our practice? The most direct approach is simply asking staff, combined with a technical review of network and device activity to identify any AI tool usage that isn’t part of a sanctioned system.
Vertascale, based in Gainesville, Georgia, helps medical and dental practices deploy HIPAA-aligned AI that reduces no-shows and front-desk overload while keeping patient data secure.
Get in Touch for a Tailored Solution
At Vertascale, we're more than just an IT provider — we're your partner in security and growth. We'll take care of your IT and cybersecurity so you can focus on your business.
Contact Us Call 470-778-0705